01 Record
CVE-2026-8254
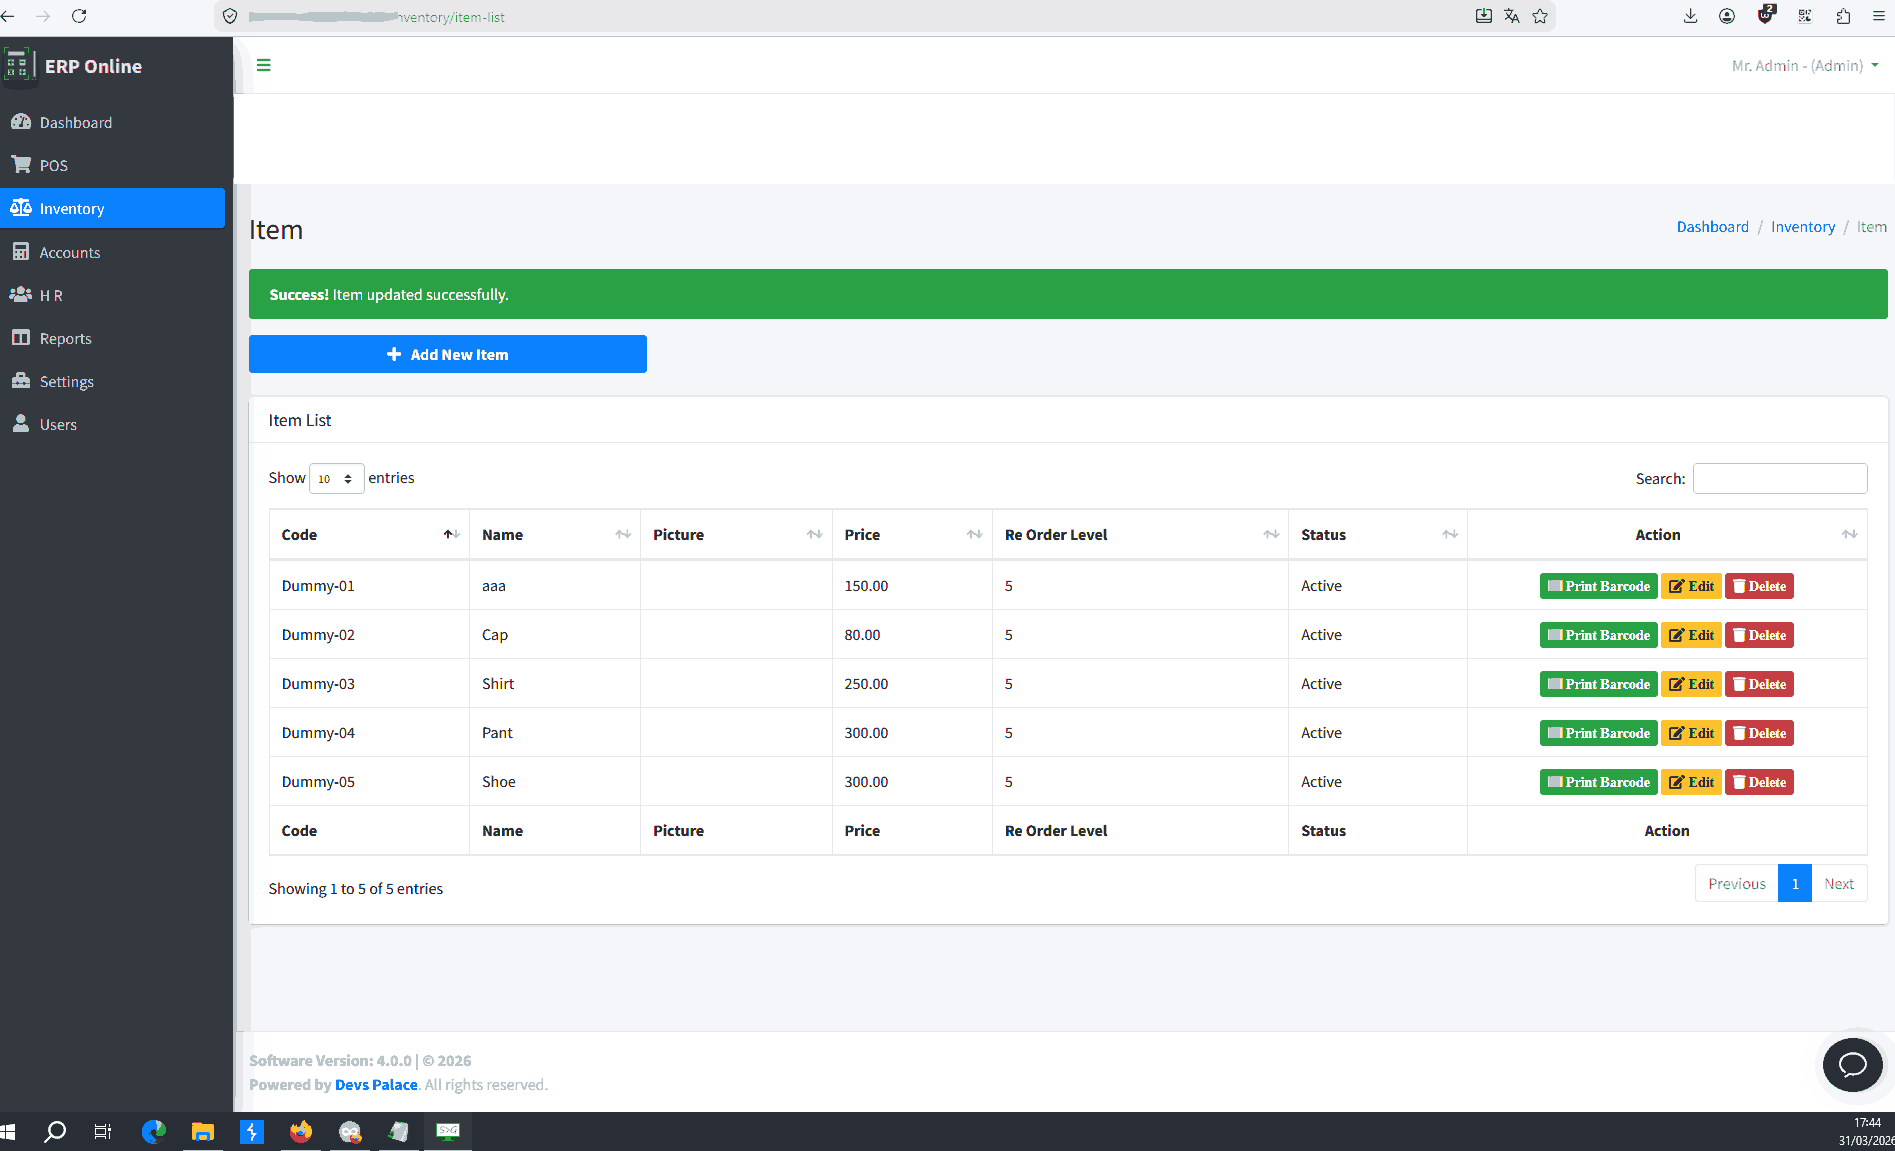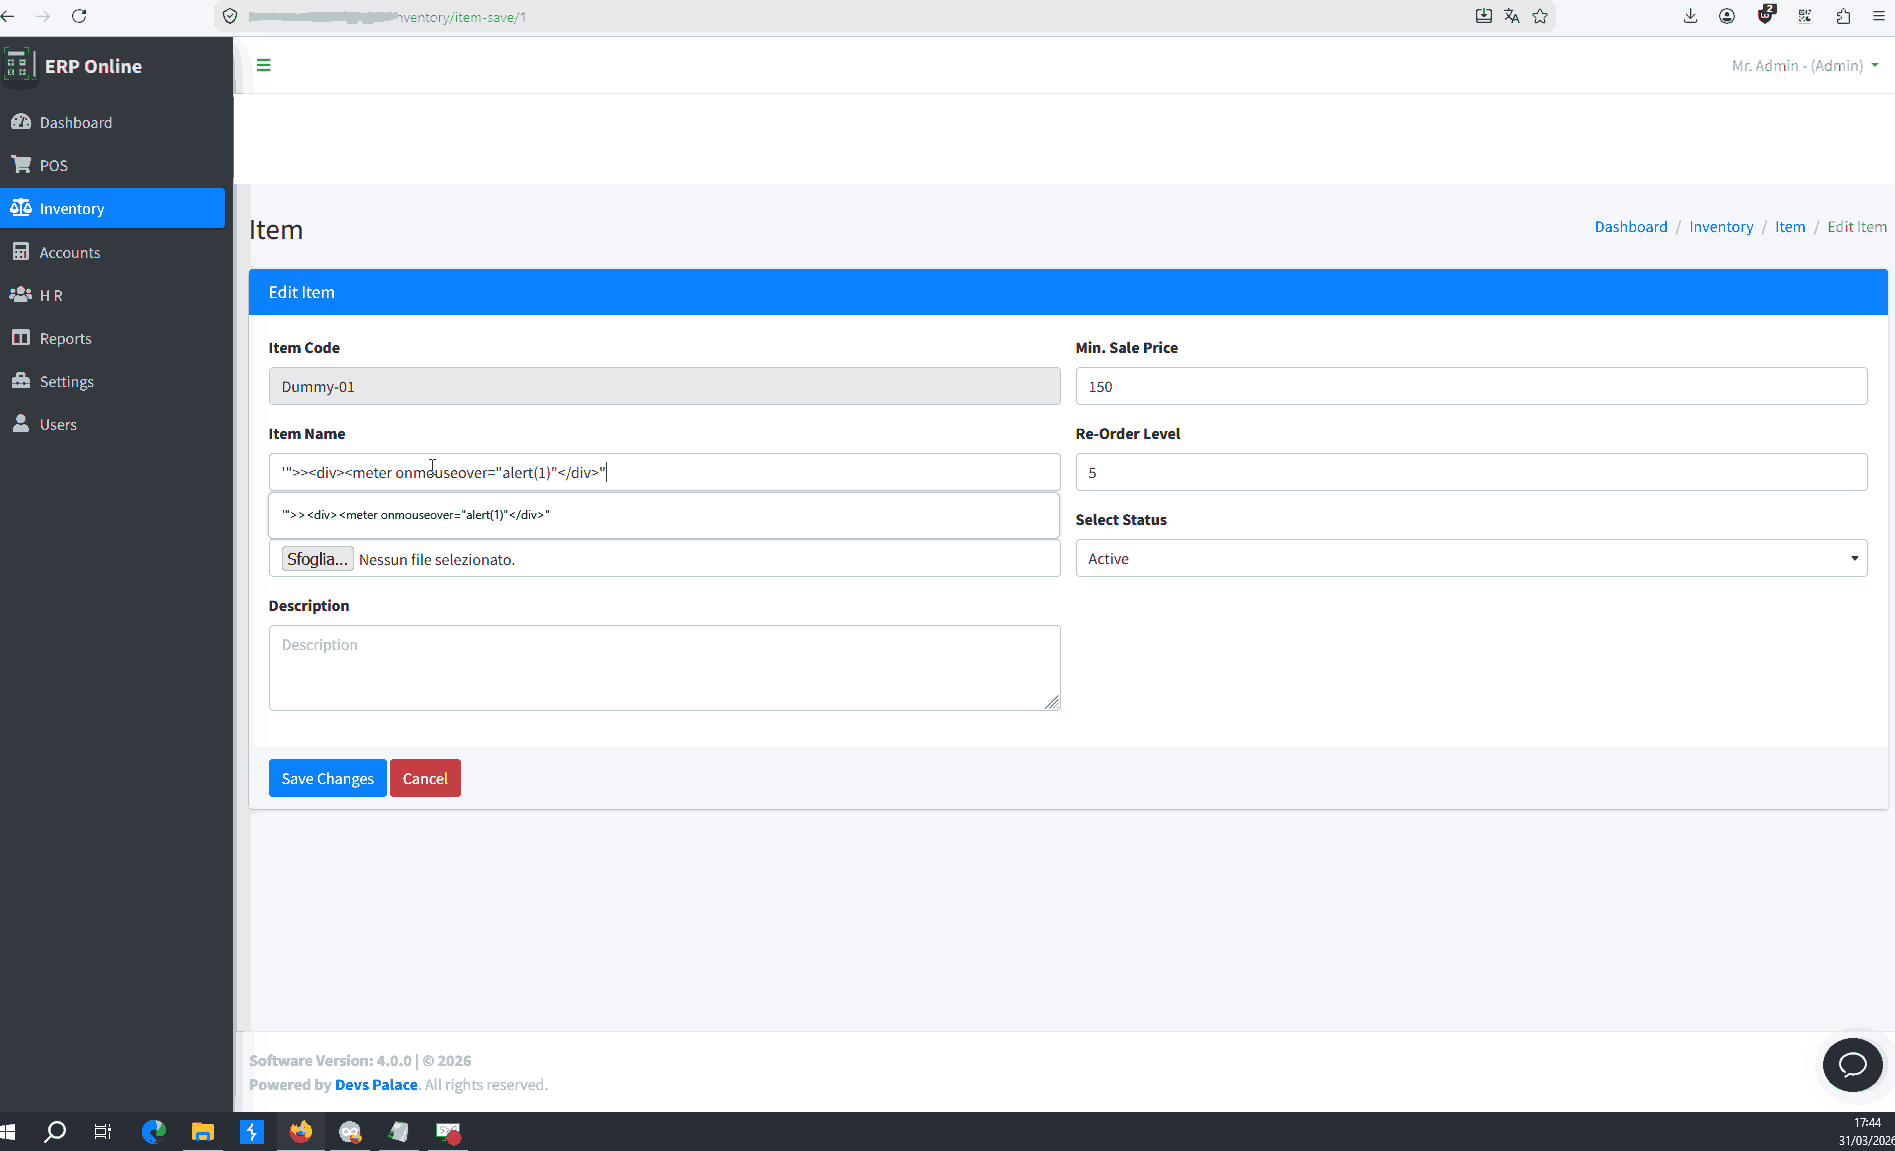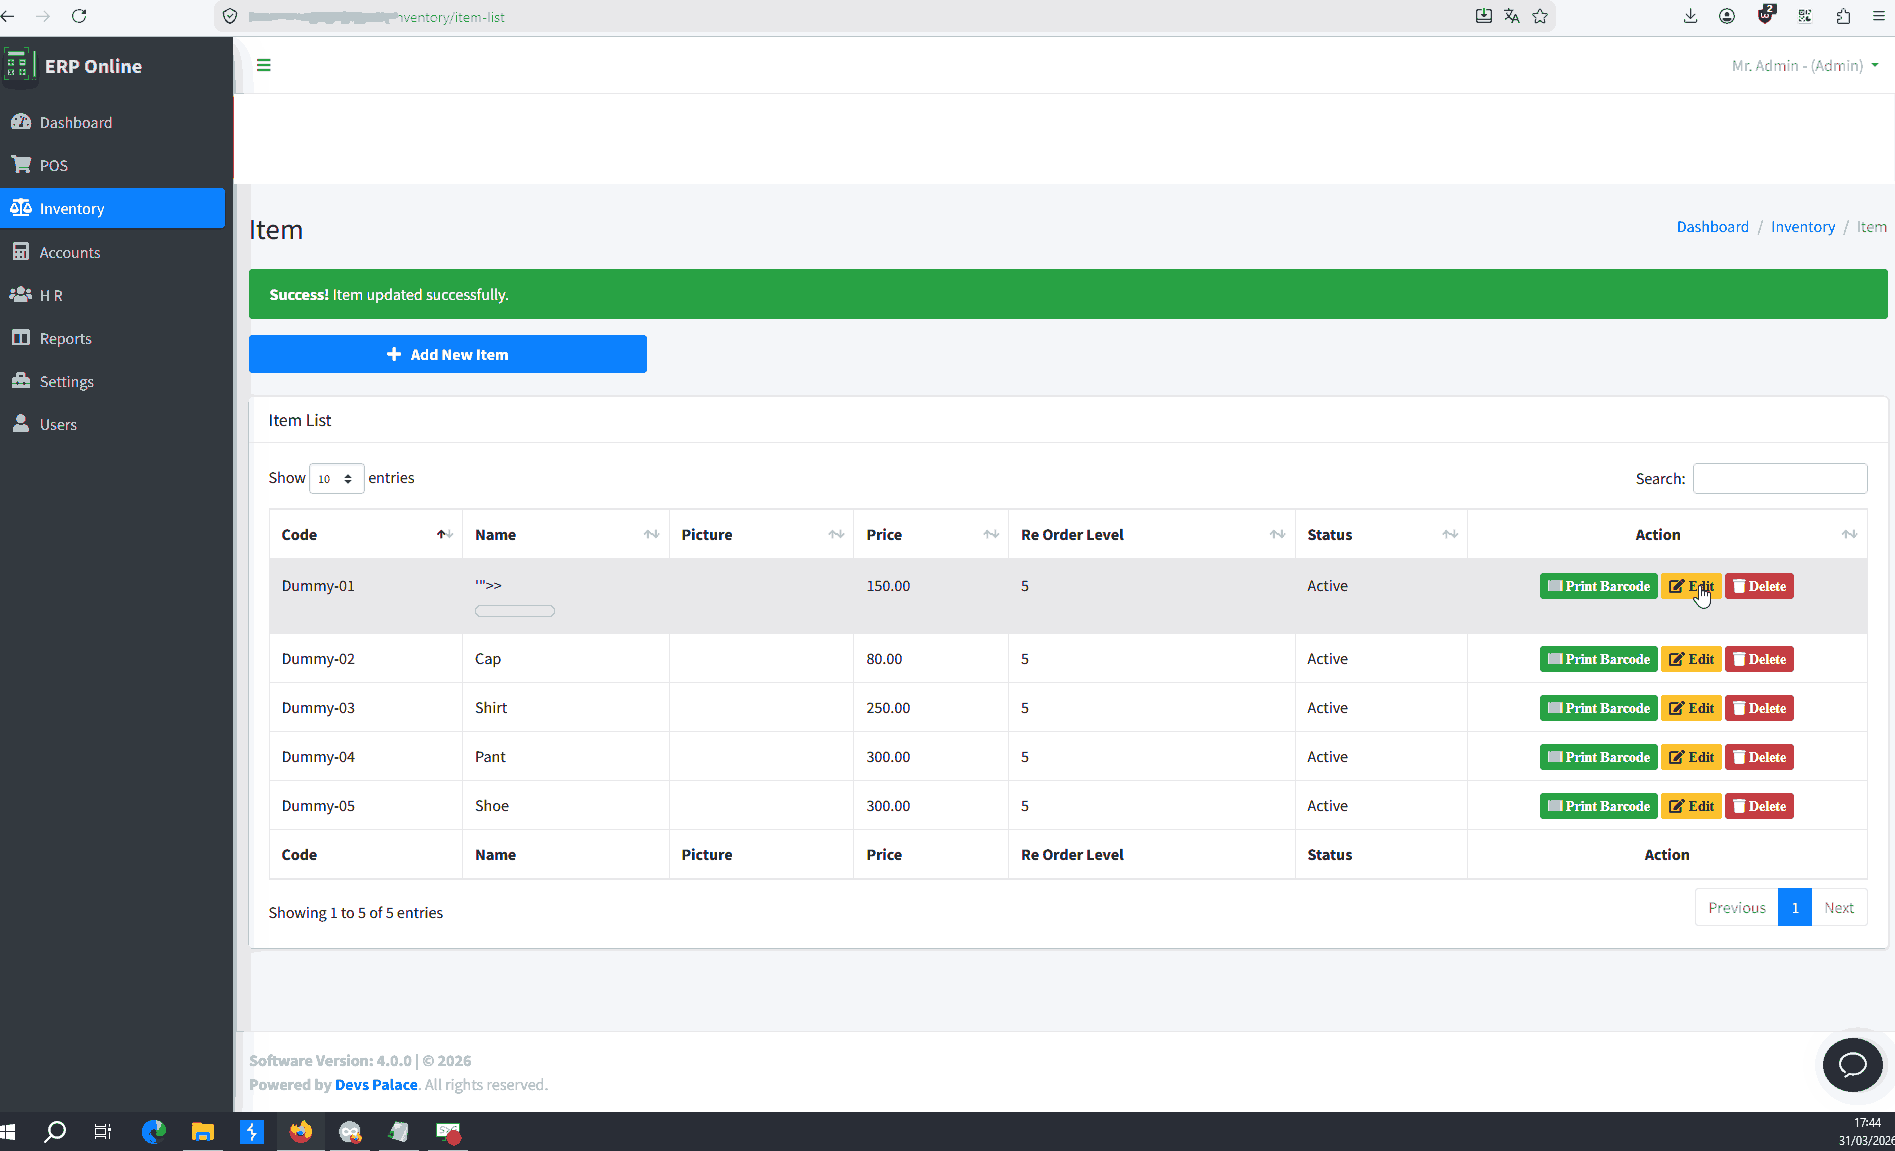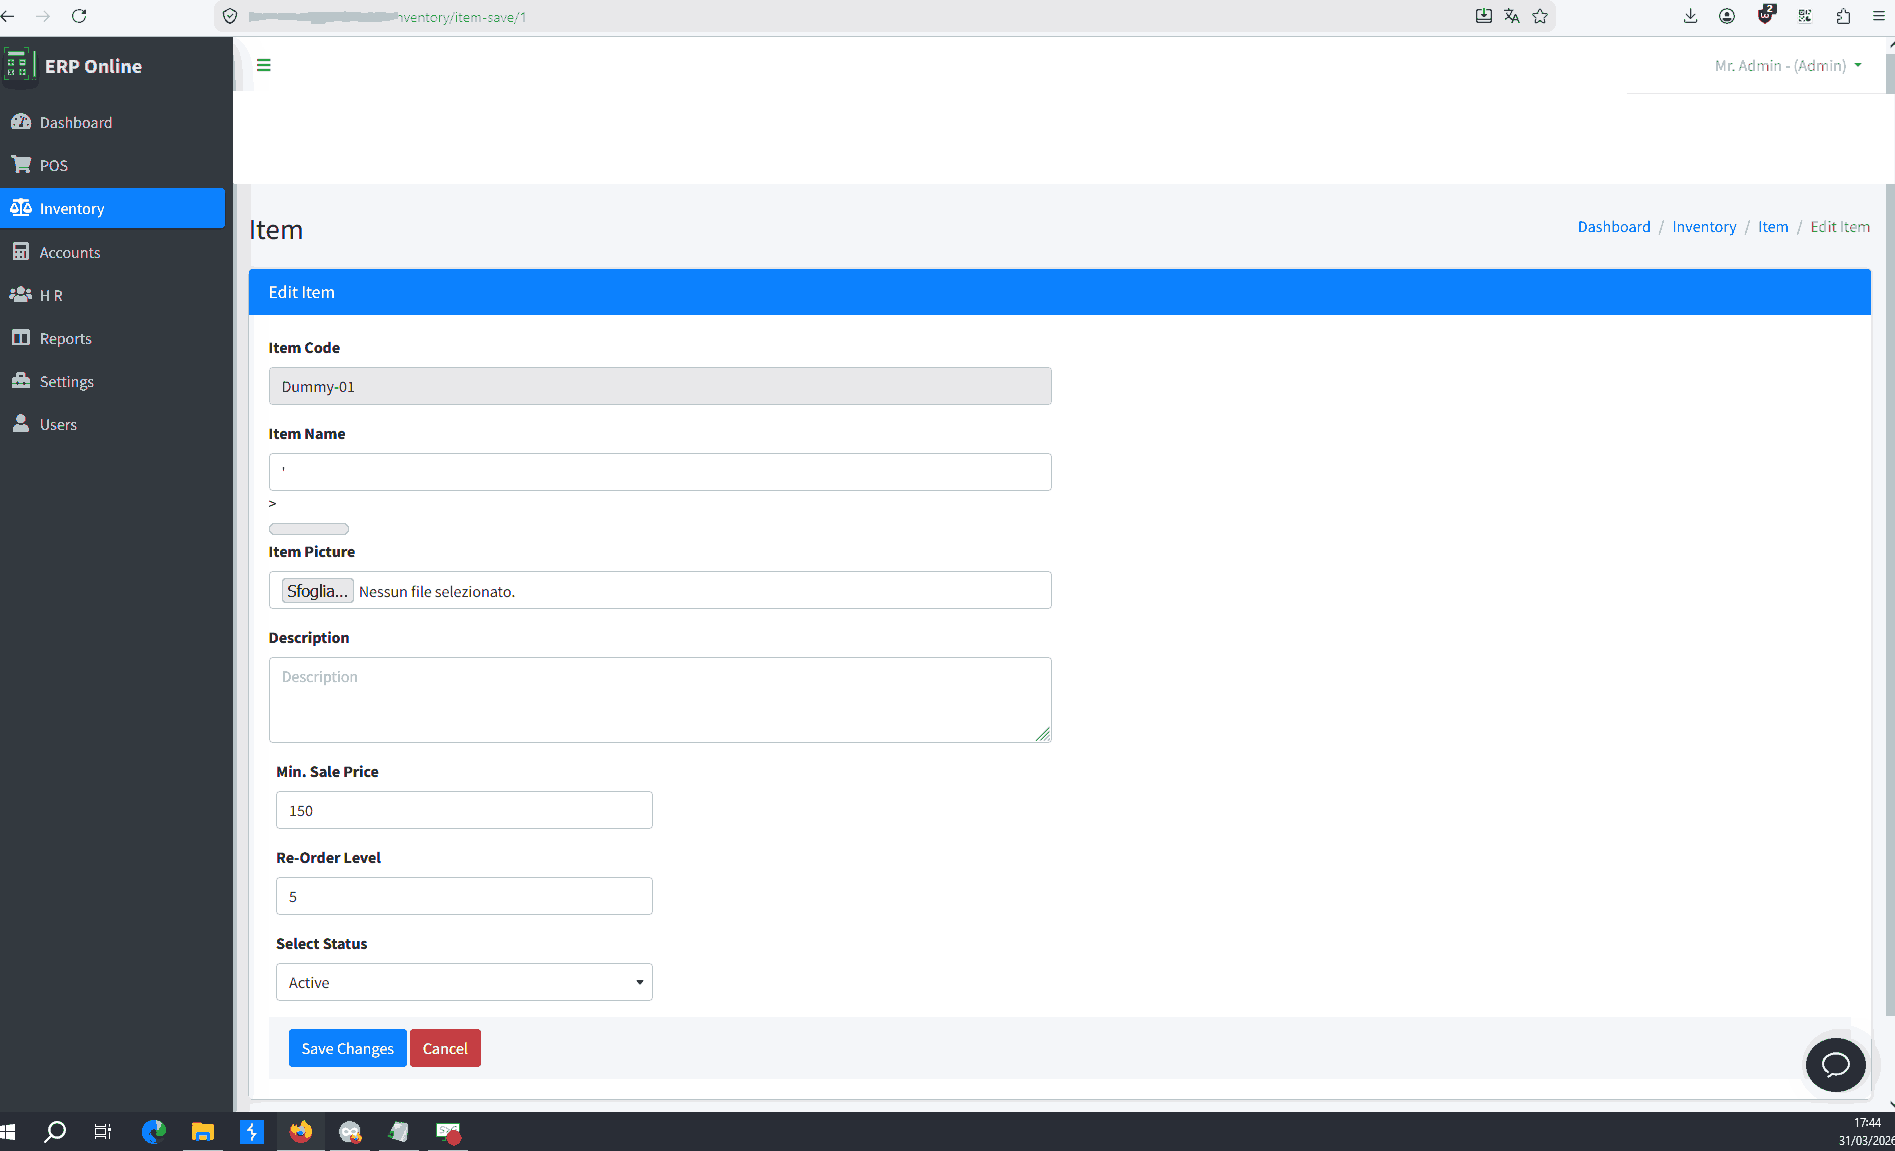
Devs Palace ERP Online sales_save cross site scripting
MediumPUBLISHEDCNA: VulDB
CNA base score4.8 CVSS v4.0CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P
02 Description
Devs Palace ERP Online sales_save cross site scripting
03 Exploitation and scoring
- Exploitation
- Public exploit code exists. CISA's assessment records a public proof of concept. That is not a report of exploitation in the wild.
- SSVC decision
- ExploitationpocPublic proof-of-concept exploit code exists. Not a report of exploitation in the wild.
- AutomatablenoAt least one step from reconnaissance to exploitation cannot be reliably automated.
- Technical ImpactpartialSuccessful exploitation gives limited control of the vulnerable component.
- EPSS probability
- 0.25% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 16.6% of scored records. A rank, not a probability.
- NVD base score
- 1.9 (CVSS v4.0), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X
- NVD analysis status
- Deferred. NVD last modified this record on 2026-07-24.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2026-05-10 23:45Z5 MO AGO
- Last updated
- 2026-05-12 02:42Z5 MO AGO
- Reserved
- 2026-05-10
- Assigning CNA
- VulDB
- Record state
- PUBLISHED
- Severity
- Medium (CVSS 4.8)
- CNA CVSS vector
- CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P
- Weaknesses
- Data version
- 5.2
- Document digest
- 4d24460f2d123d7f828471007af0d4762db524760220f908e0ef5b4cddbf3e6a
05 Affected products
VendorProductVersionsPlatforms
06 References
- vuldb.comVDB-362551 | Devs Palace ERP Online sales_save cross site scriptinghttps://vuldb.com/vuln/362551
- vuldb.comVDB-362551 | CTI Indicators (IOB, IOC, TTP, IOA)https://vuldb.com/vuln/362551/cti
- vuldb.comSubmit #808279 | Devs Palace ERP Online 4.0.0 Code Injectionhttps://vuldb.com/submit/808279
- olografix.orghttps://olografix.org/acme/_poc/ERP_Online-POC1.gif