01 Record
CVE-2024-25730
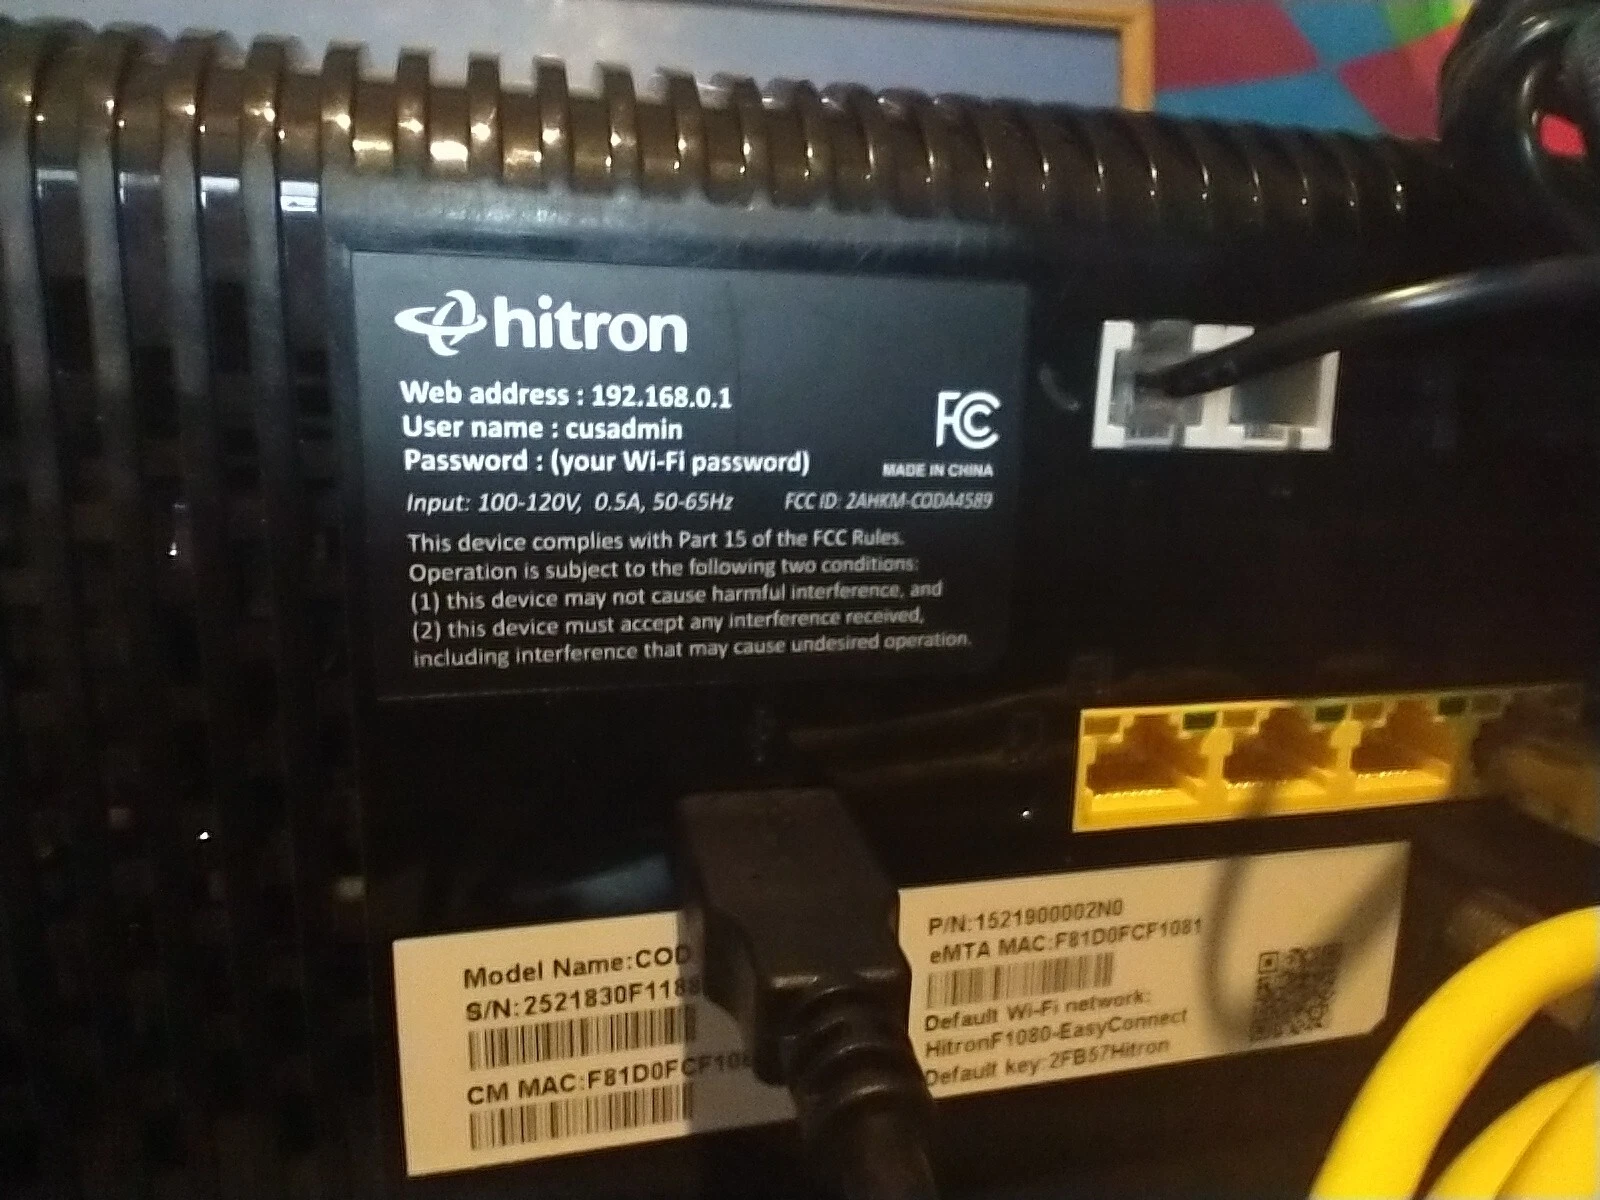
Hitron CODA-4582 and CODA-4589 devices have default PSKs that are generated from 5-digit hex values concatenated with a "Hitron" substring, resulting in insufficient entropy (only about one million
CriticalPUBLISHEDCNA: mitre
CNA base score9.8 CVSS v3.xCVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
02 Description
Hitron CODA-4582 and CODA-4589 devices have default PSKs that are generated from 5-digit hex values concatenated with a "Hitron" substring, resulting in insufficient entropy (only about one million
03 Exploitation and scoring
- Exploitation
- Assessed, none found. CISA's assessment recorded neither public exploit code nor evidence of exploitation when it was made.
- SSVC decision
- ExploitationnoneCISA recorded no public exploit code and no evidence of exploitation.
- AutomatableyesAn attacker can reliably automate reconnaissance through exploitation, so this scales.
- Technical ImpacttotalSuccessful exploitation gives total control of the vulnerable component.
- EPSS probability
- 0.86% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 58.2% of scored records. A rank, not a probability.
- NVD base score
- 9.8 (CVSS v3.x), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
- NVD analysis status
- Analyzed. NVD last modified this record on 2026-06-17.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2024-02-23 00:00Z2 YR AGO
- Last updated
- 2024-08-16 17:14Z2 YR AGO
- Reserved
- 2024-02-11
- Assigning CNA
- mitre
- Record state
- PUBLISHED
- Severity
- Critical (CVSS 9.8)
- CNA CVSS vector
- CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
- Weaknesses
- CWE-331Insufficient EntropyBase
- Data version
- 5.1
- Document digest
- 35ed89a6b75868ec74dcb30dc9ded91546f8ab01f0d4fc2737ccbbe467d92d06
05 Affected products
VendorProductVersionsPlatforms
06 References
- i.ebayimg.comhttps://i.ebayimg.com/images/g/I-8AAOSwGE9lsGwI/s-l1600.webp
- i.ebayimg.comhttps://i.ebayimg.com/images/g/qK8AAOSwbr9lq3PJ/s-l1600.webp
- i.ebayimg.comhttps://i.ebayimg.com/images/g/VDcAAOSwlodlSuz4/s-l1600.webp
- i.ebayimg.comhttps://i.ebayimg.com/images/g/MwMAAOSwjTFk3kpd/s-l1600.webp
- i.ebayimg.comhttps://i.ebayimg.com/images/g/XaAAAOSwvMNkuESk/s-l1600.webp
- i.ebayimg.comhttps://i.ebayimg.com/images/g/hzUAAOSwUwVllGMZ/s-l1600.webp
- github.comhttps://github.com/actuator/cve/blob/main/Hitron/CVE-2024-25730