01 Record
CVE-2022-23884
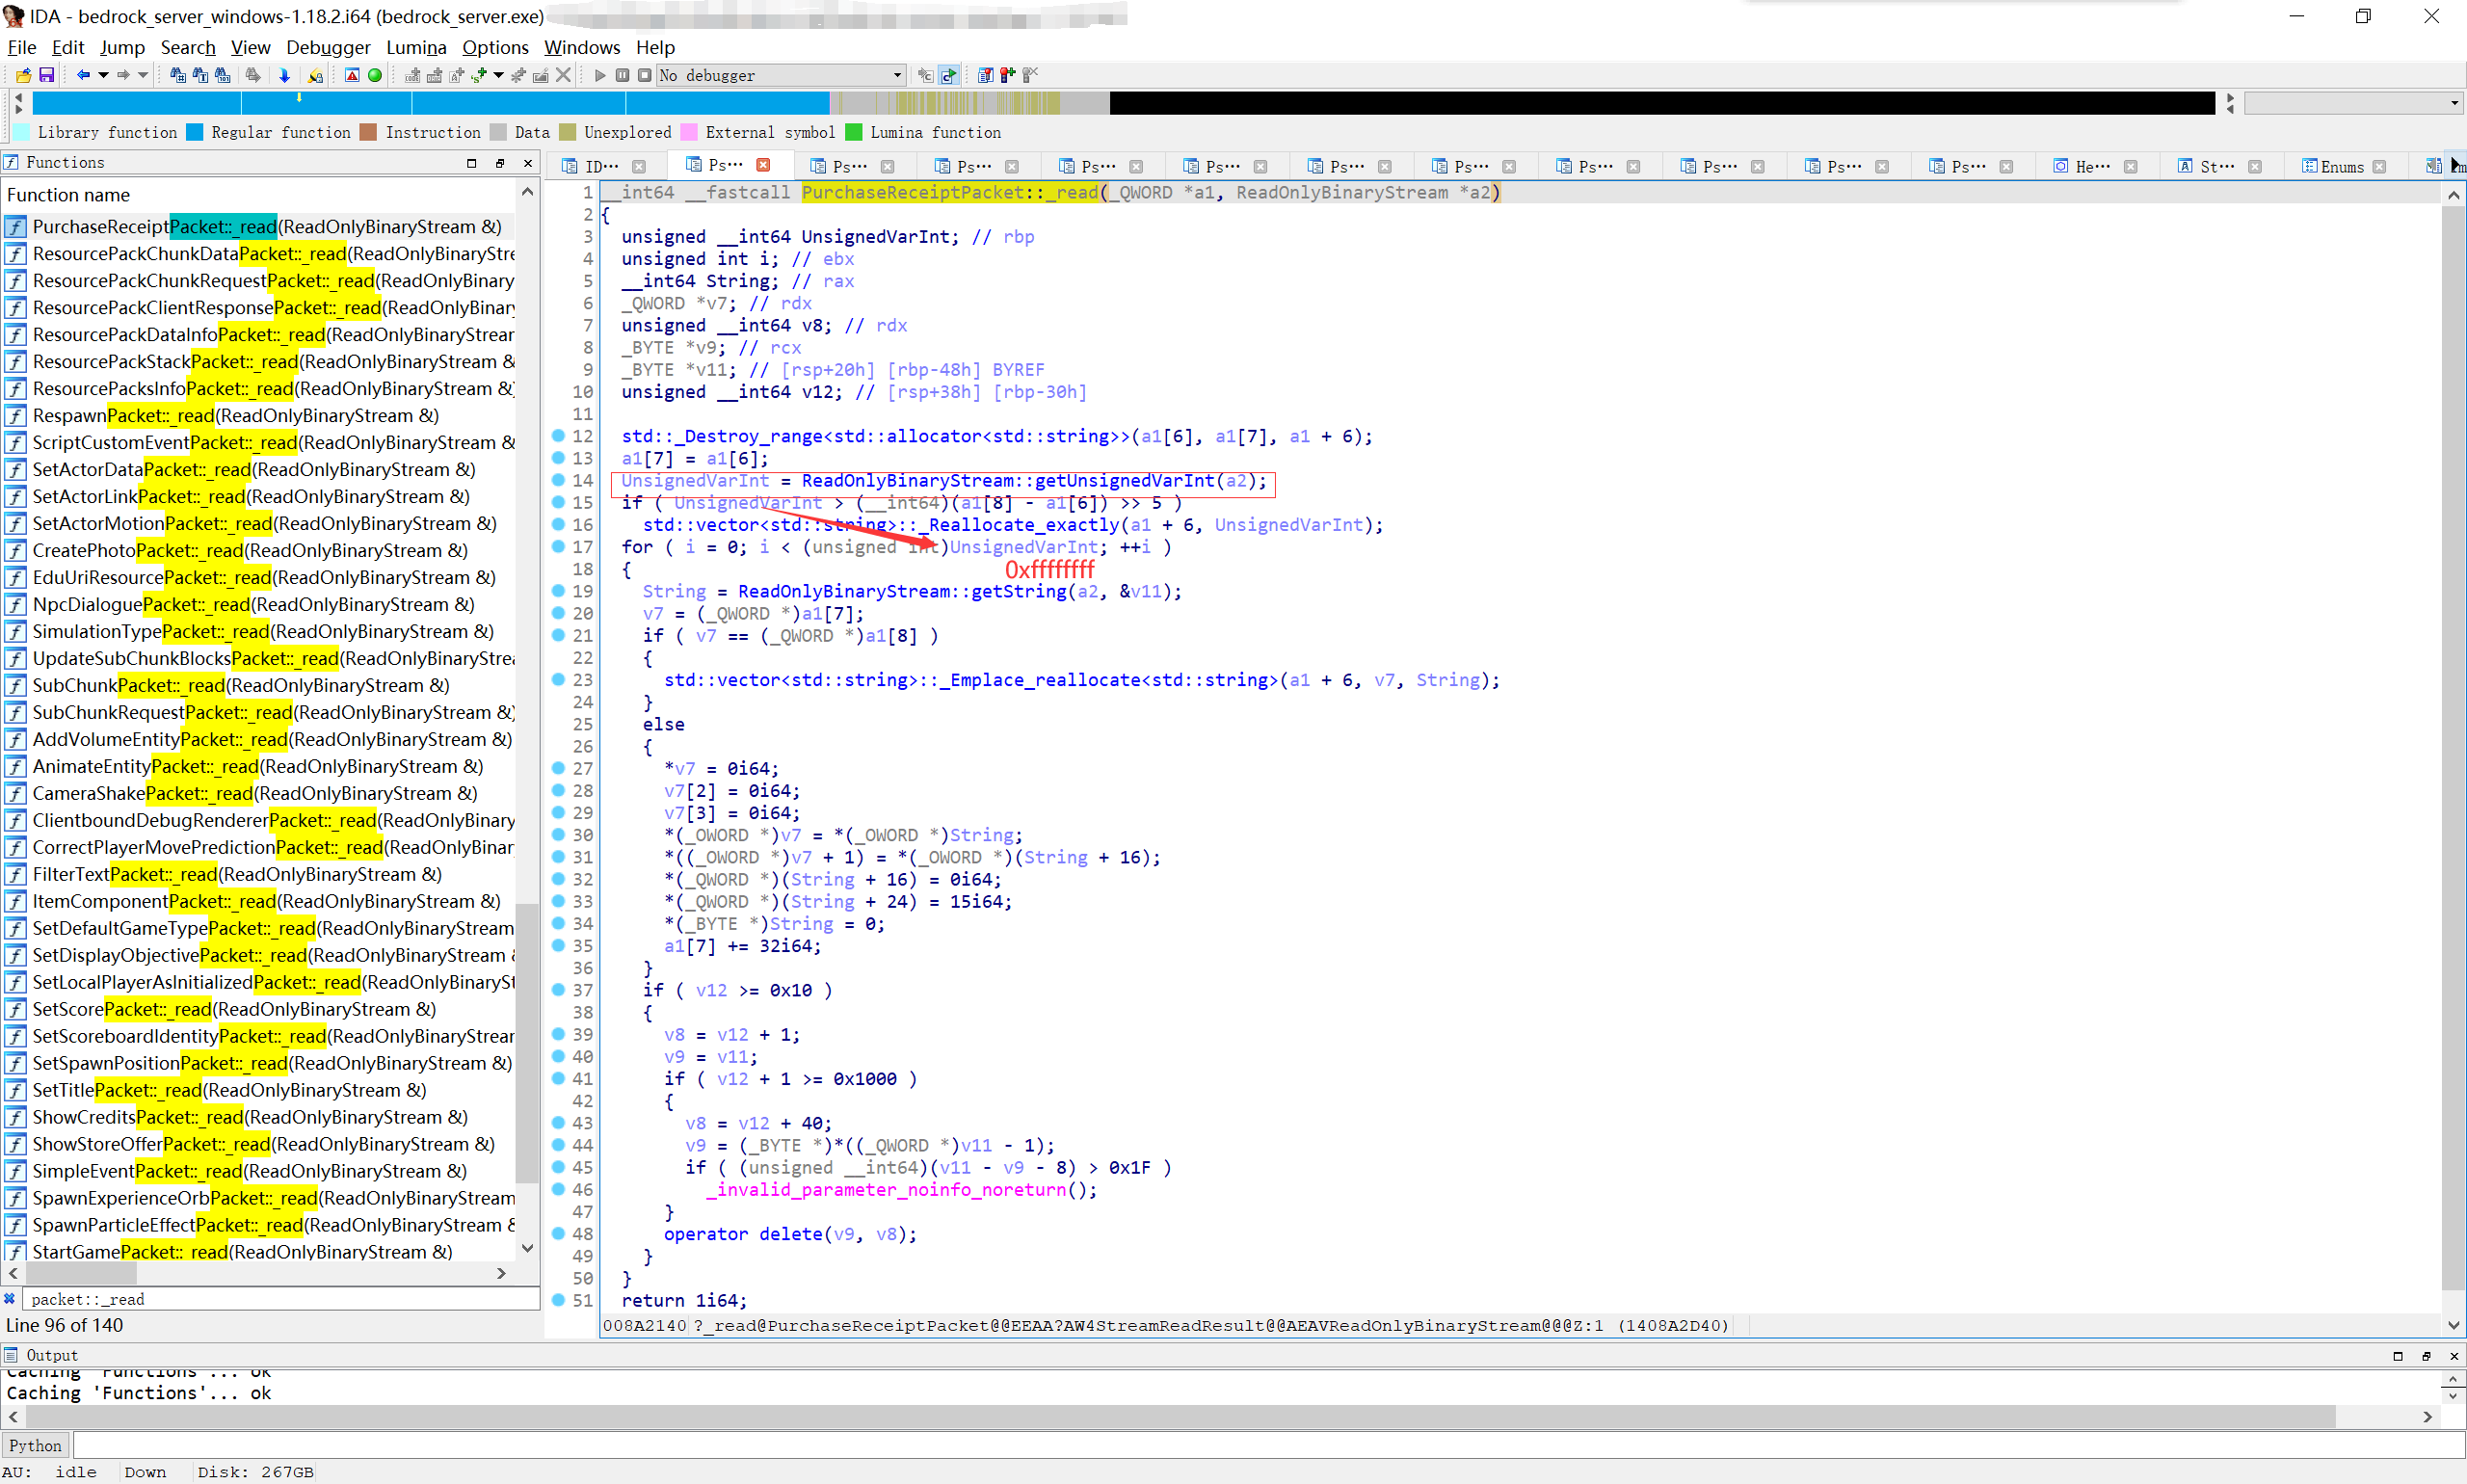
Mojang Bedrock Dedicated Server 1.18.2 is affected by an integer overflow leading to a bound check bypass caused by PurchaseReceiptPacket::_read (packet deserializer).
UnratedPUBLISHEDCNA: mitre
CNA base scoreUnratedNo CNA CVSS vector
02 Description
Mojang Bedrock Dedicated Server 1.18.2 is affected by an integer overflow leading to a bound check bypass caused by PurchaseReceiptPacket::_read (packet deserializer).
03 Exploitation and scoring
- Exploitation
- Not assessed. CISA has not published an exploitation assessment for this record, and it is not in the KEV catalog. That is an absence of assessment, not a finding of no risk.
- SSVC decision
- Not assessed by CISA
- EPSS probability
- 2.58% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 85.1% of scored records. A rank, not a probability.
- NVD base score
- 9.8 (CVSS v3.x), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
- NVD analysis status
- Modified. NVD last modified this record on 2026-06-17.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2022-03-28 12:08Z4 YR AGO
- Last updated
- 2024-08-03 03:59Z2 YR AGO
- Reserved
- 2022-01-24
- Assigning CNA
- mitre
- Record state
- PUBLISHED
- Severity
- Not rated by the issuing CNA
- CNA CVSS vector
- Not published by the issuing CNA
- Weaknesses
- CWE-190Integer Overflow or WraparoundBase
- Data version
- 5.1
- Document digest
- a3c60c7c7b4d2b6c9290f9d6a864938e4aa8e6078b1ce83706974d644e781673
05 Affected products
VendorProductVersionsPlatforms