01 Record
CVE-2018-19981
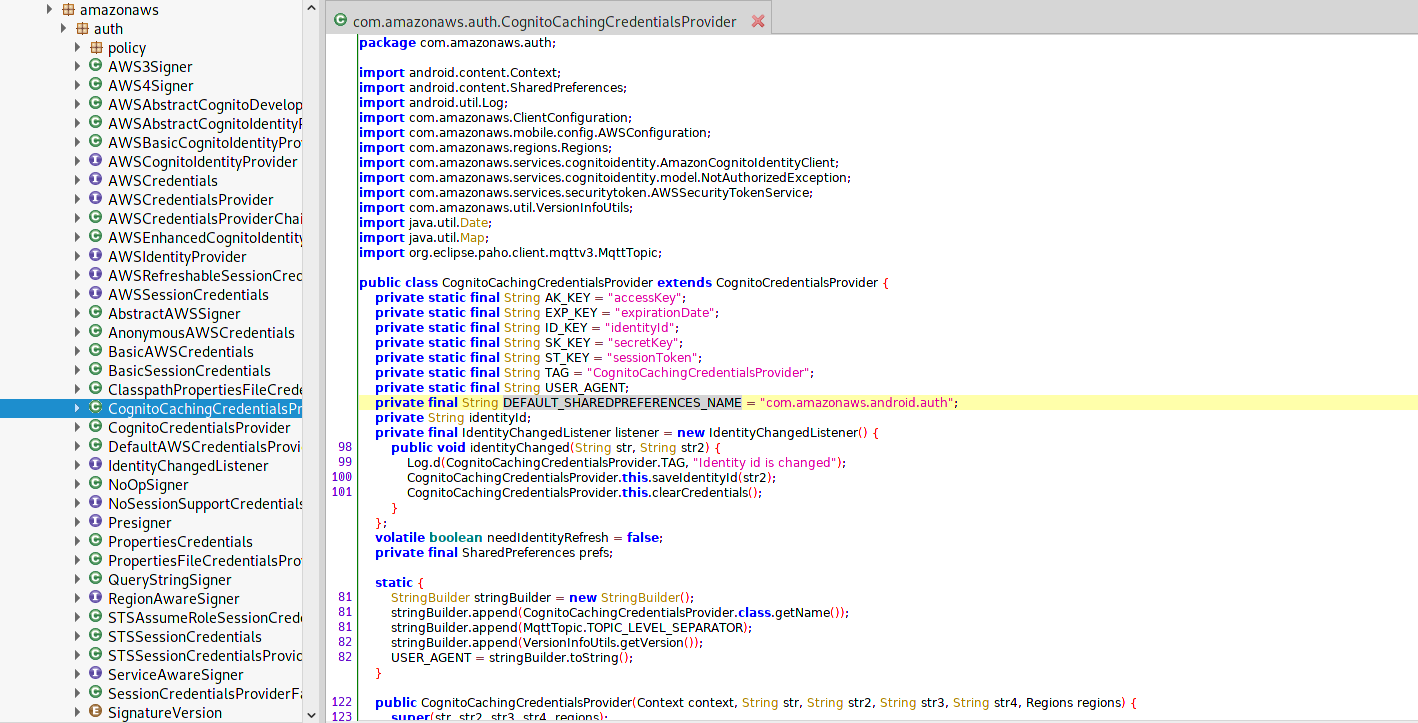
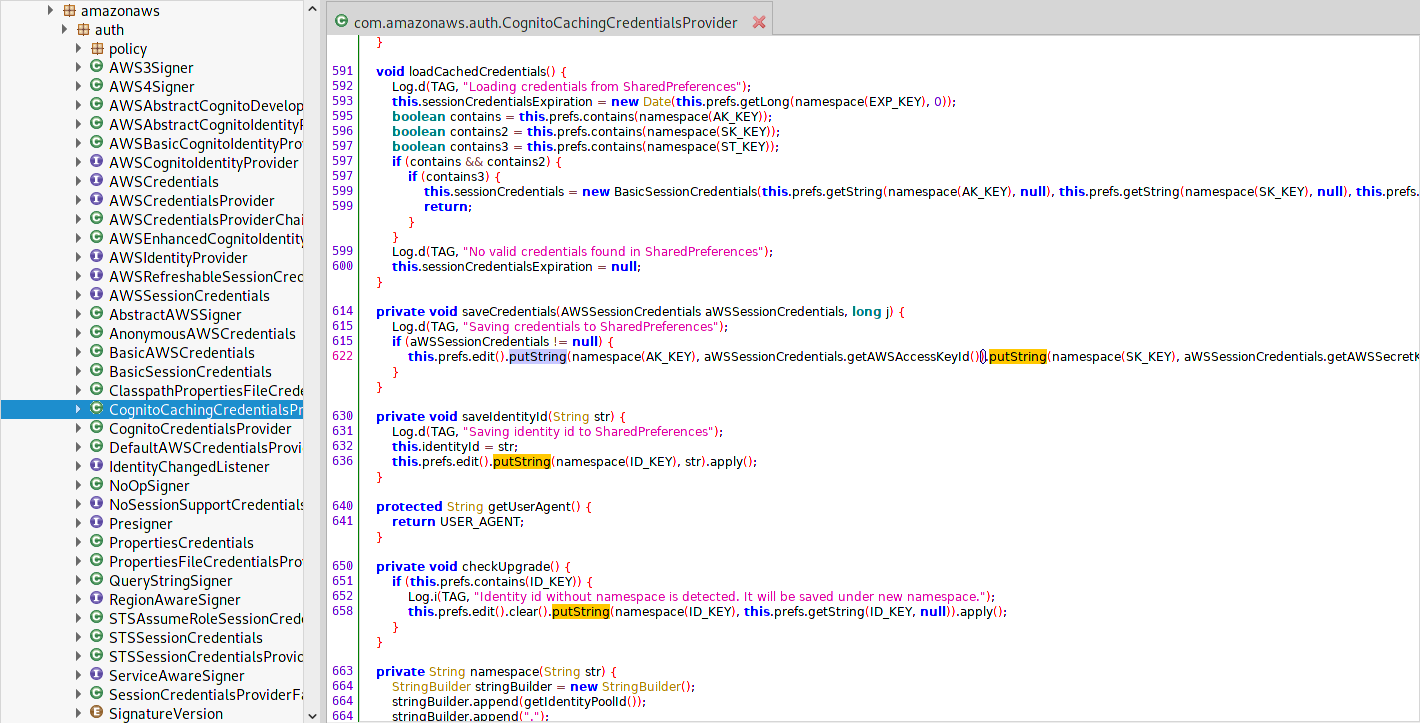
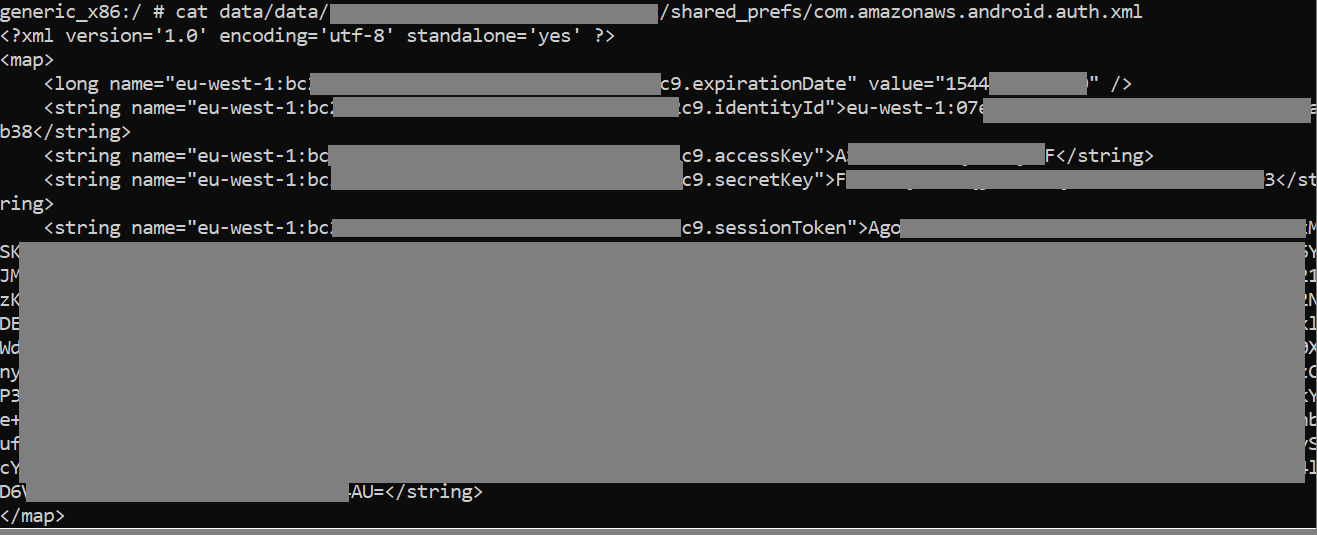
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to
UnratedPUBLISHEDCNA: mitre
CNA base scoreUnratedNo CNA CVSS vector
02 Description
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to
03 Exploitation and scoring
- Exploitation
- Not assessed. CISA has not published an exploitation assessment for this record, and it is not in the KEV catalog. That is an absence of assessment, not a finding of no risk.
- SSVC decision
- Not assessed by CISA
- EPSS probability
- 1.79% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 78.0% of scored records. A rank, not a probability.
- NVD base score
- 7.2 (CVSS v3.x), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H
- NVD analysis status
- Modified. NVD last modified this record on 2026-06-17.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2019-04-04 14:34Z7 YR AGO
- Last updated
- 2024-08-05 11:51Z2 YR AGO
- Reserved
- 2018-12-09
- Assigning CNA
- mitre
- Record state
- PUBLISHED
- Severity
- Not rated by the issuing CNA
- CNA CVSS vector
- Not published by the issuing CNA
- Weaknesses
- CWE-312Cleartext Storage of Sensitive InformationBase
- Data version
- 5.1
- Document digest
- e2bbd96b929a89fd58a89683d65cca8af224c0e6772510bb10da32437e284112
05 Affected products
VendorProductVersionsPlatforms
06 References
- raw.githubusercontent.comhttps://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
- raw.githubusercontent.comhttps://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_02.png
- raw.githubusercontent.comhttps://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_03.png
- aws-amplify.github.iohttps://aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html