01 Record
CVE-2018-19461
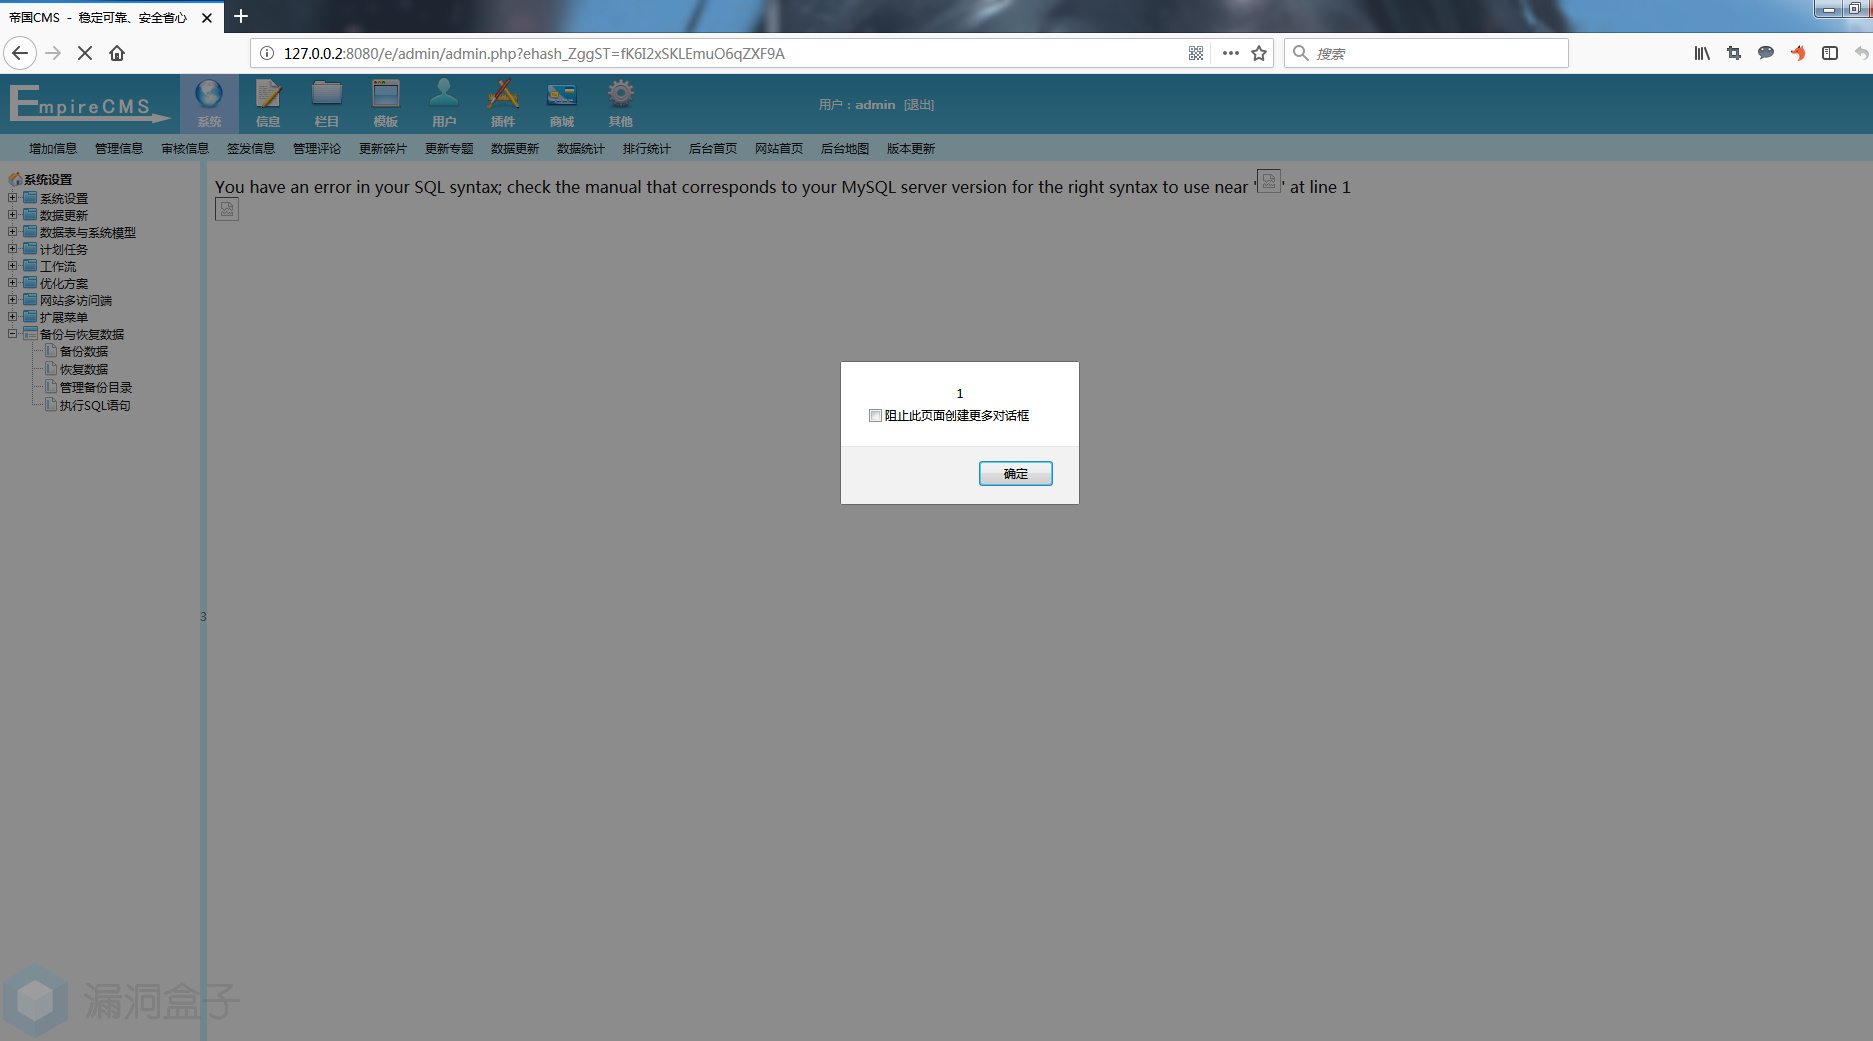
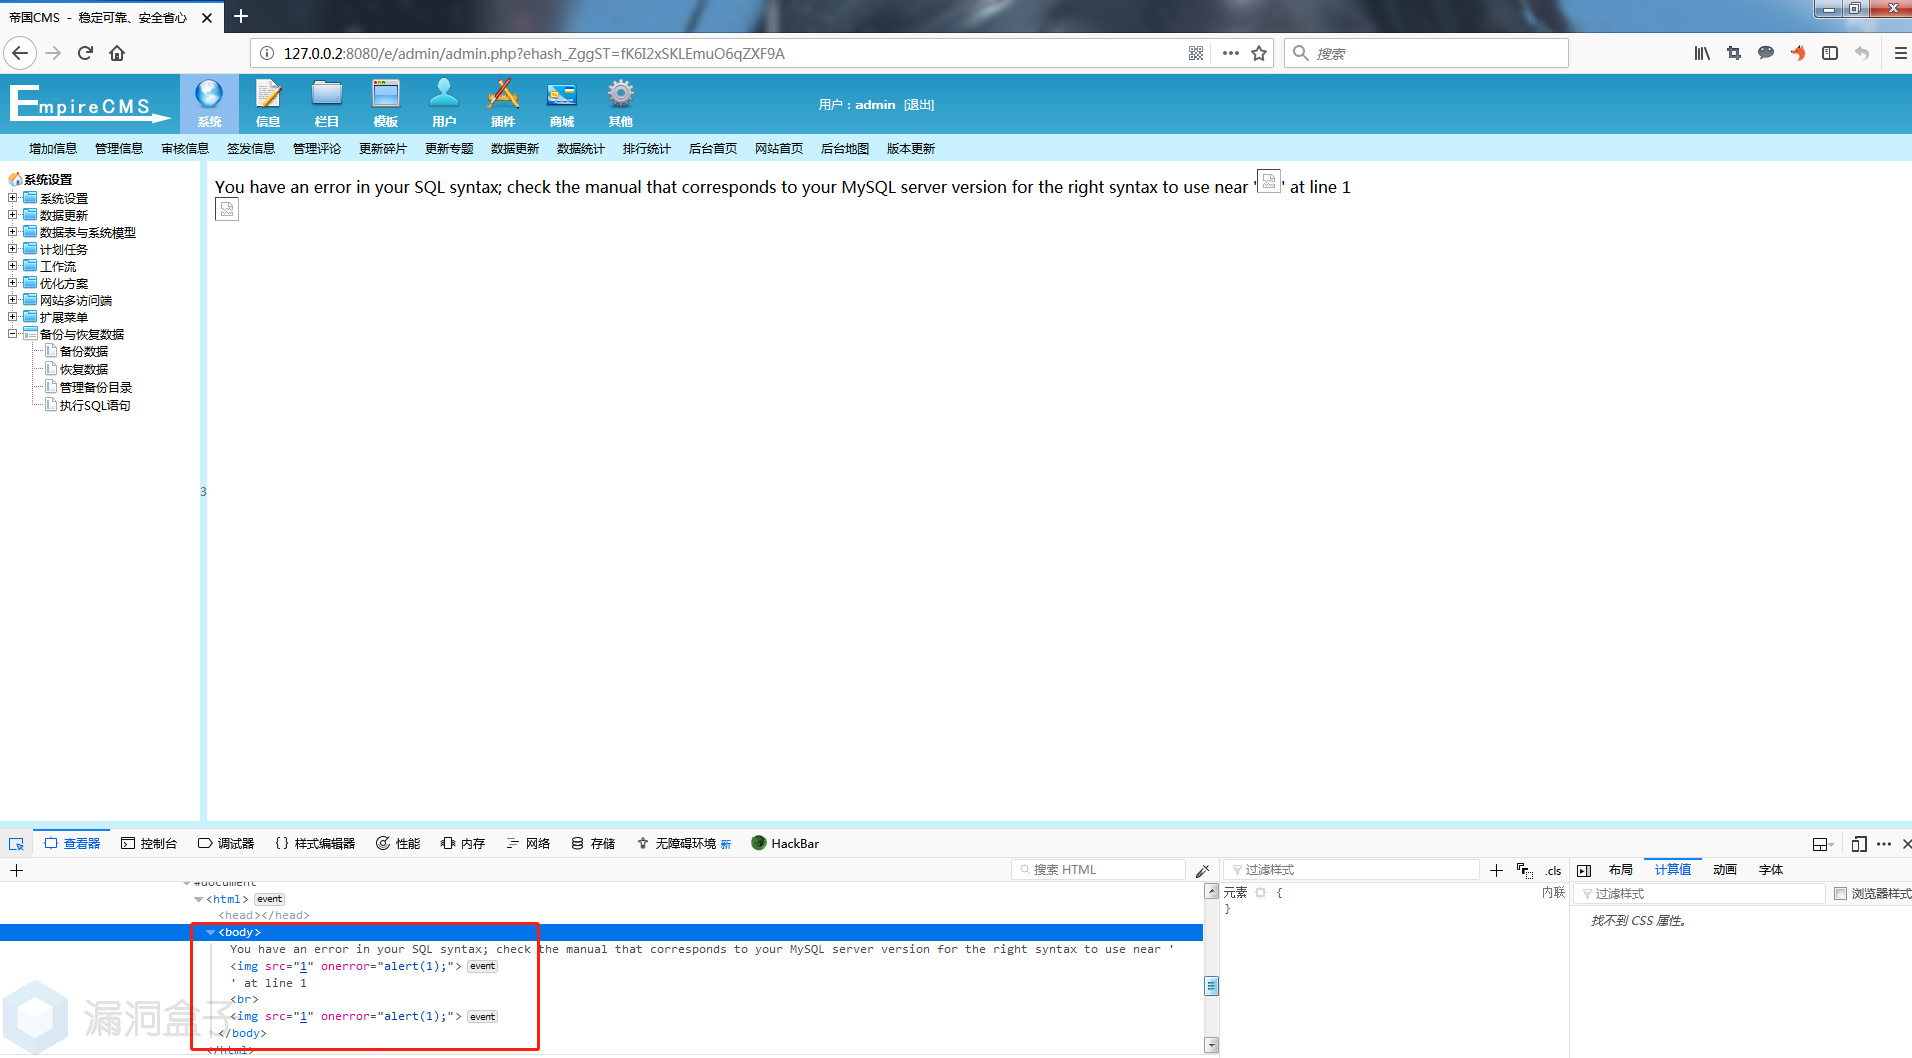
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
UnratedPUBLISHEDCNA: mitre
CNA base scoreUnratedNo CNA CVSS vector
02 Description
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
03 Exploitation and scoring
- Exploitation
- Not assessed. CISA has not published an exploitation assessment for this record, and it is not in the KEV catalog. That is an absence of assessment, not a finding of no risk.
- SSVC decision
- Not assessed by CISA
- EPSS probability
- 0.91% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 59.7% of scored records. A rank, not a probability.
- NVD base score
- 4.8 (CVSS v3.x), scored by the NVD independently of the CNA.
- NVD CVSS vector
- CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N
- NVD analysis status
- Modified. NVD last modified this record on 2026-06-17.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2019-06-07 16:46Z7 YR AGO
- Last updated
- 2024-08-05 11:37Z2 YR AGO
- Reserved
- 2018-11-22
- Assigning CNA
- mitre
- Record state
- PUBLISHED
- Severity
- Not rated by the issuing CNA
- CNA CVSS vector
- Not published by the issuing CNA
- Weaknesses
- CWE-79Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')Base
- Data version
- 5.1
- Document digest
- ac85f1f86a7b85472d3cd6ef6a0f26e445569369b5c81ed6e1918a21c4420c0c
05 Affected products
VendorProductVersionsPlatforms